DNSSEC (DNS Security Extensions) adds a layer of authentication to DNS by validating digital signatures across a chain of trust, from the DNS root to the specific record being requested. It protects against cache poisoning attacks, where an attacker redirects users to a malicious site even when a valid web address is entered.
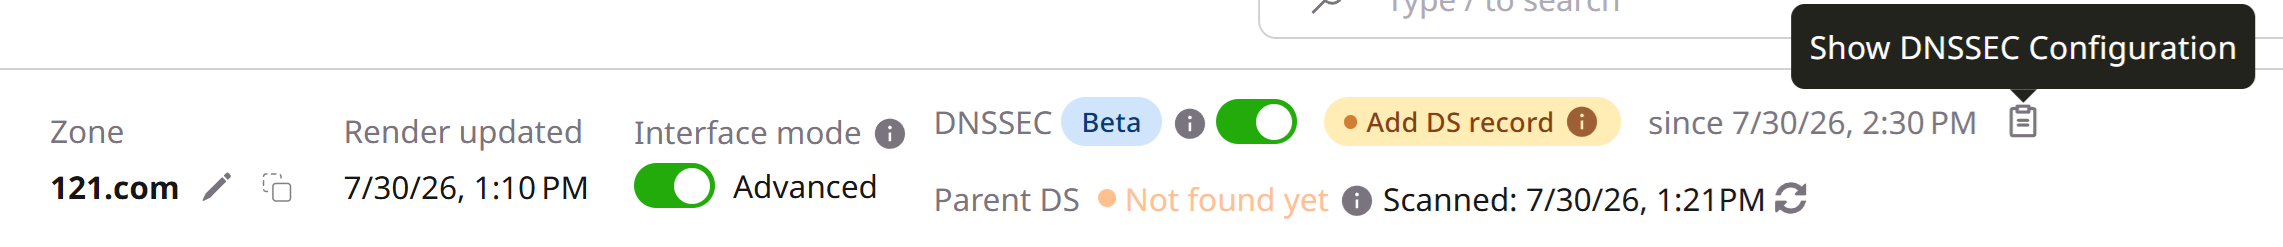
Turn on Interface mode → Advanced (see interface modes). The DNSSEC control appears in the zone header with a Beta label.
Turn on the DNSSEC toggle.
In the confirmation dialog, type the zone name to confirm, then click Yes, enable.
The DNSSEC Configuration dialog opens and shows the DS record details for the zone — copy the value in the DS record field.
Paste the DS record value into the domain registrar's control panel.
💡
If transferring a DNS zone from another provider, disable DNSSEC at the old provider first and wait for the DS record TTL to expire before enabling it here.
DS propagation can take up to an hour at most registrars, and up to 24 hours in some cases. While waiting for DS confirmation, the DNSSEC toggle stays on and the zone header shows Add DS record, the activation time (since), and Parent DS as Not found yet — this is the transitional pending state, not disabled. After CDB detects the DS record at the registrar, Parent DS updates and the zone status becomes active.
ℹ️
To view the DS record again, click the Show DNSSEC Configuration icon next to the activation date in the zone header.
DNSSEC status lifecycle
After enabling DNSSEC, the zone moves through a lifecycle driven by what CDB observes at the domain registrar — not only by the enable or disable request. CDB periodically scans the registrar for the DS record and updates the zone's DNSSEC status. The Customer Portal shows each transitional and stable state from the backend — for example, pending appears with the toggle on plus Add DS record and Parent DS status, not as a plain off/disabled toggle.
Status
Meaning
What the Portal shows
Action required
pending
DNSSEC is enabled, signing keys are generated, but CDB has not yet detected the DS record at the registrar
Toggle on, Add DS record, activation time, Parent DS not yet confirmed (Not found yet)
Add the DS record CDB provided to the registrar
active
A valid DS record is detected at the registrar. The chain of trust is established
Toggle on, confirmed Parent DS
None — DNSSEC is working
pending-disabled
DNSSEC is disabled and the signing keys are removed, but CDB has not yet detected that the DS record has been removed from the registrar
Transitional disable state (distinct from fully disabled)
Remove the DS record at the registrar to complete the process
disabled
DNSSEC is off and no DS record is present
Toggle off
None
The transition from pending to active can take from a few minutes to several hours, depending on the registrar's propagation speed and the DS record's TTL. Once active, the status remains active — removing the DS record at the registrar does not automatically change it.
Disable DNSSEC
⚠️
Remove the DS record from your registrar before disabling DNSSEC in CDB. If DNSSEC is disabled in CDB while the DS record is still published, resolvers will try to validate signatures that no longer exist, causing DNS resolution failures.
Remove the DS record from the domain registrar's control panel.
Wait for the DS record TTL to expire so cached records clear.
In the CDB Technical Web Portal, navigate to DNS > All zones, open the zone, and turn off the DNSSEC toggle. In the confirmation dialog, type the zone name to confirm, then click Yes, disable.
If disable is requested while a DS record is still published at the registrar, the zone moves to pending-disabled. The Portal keeps that transitional state visible until the DS record is removed and the status becomes disabled.
The DNS API supports enabling and disabling DNSSEC, retrieving DS records, checking zone status, and verifying DS propagation at the registrar. The Python and Go SDKs cover enable, get DS record, and disable operations.
ℹ️
An API token is required. Set these environment variables before running the examples:
Enabling DNSSEC generates signing keys for the zone and returns the DS (Delegation Signer) record — the ds field in the response contains the complete DS record string to add at your registrar.
Copy the ds field value from the response and add it to your registrar's control panel. The zone enters the pending state until CDB detects the DS record at your registrar, which can take from a few minutes to several hours.
Get DS record
To retrieve the DS record for a zone that already has DNSSEC enabled:
The zone response includes two fields that reflect the current DNSSEC state, updated by CDB's periodic scan of your registrar:
dnssec_status — the current lifecycle state: pending, active, pending-disabled, or disabled
dnssec_status_modified_on — RFC 3339 timestamp of the last status change
Both fields are absent from the response if DNSSEC has never been enabled on the zone. A missing field is not an error — it means the zone has no DNSSEC history.
Status
Meaning
pending
DNSSEC enabled, keys generated, DS record not yet detected at the registrar
active
DS record detected at the registrar — chain of trust established
pending-disabled
Disable requested, DS record still present at the registrar
disabled
DNSSEC off, no DS record present
The transition from pending to active can take from a few minutes to several hours, depending on your registrar's propagation speed and the DS record's TTL. Once active, the status remains active — removing the DS record at the registrar does not automatically change it. To turn DNSSEC off, use the disable endpoint.
To check the current status, fetch the zone and inspect the dnssec_status field:
dnssec_status is distinct from the top-level status field — status reflects zone delegation to CDB nameservers, while dnssec_status reflects the DNSSEC lifecycle.
Check DS record at registrar
To verify whether a valid DS record is currently detected at the registrar, use the parent-ds endpoint:
If a DS record is still published at the registrar when the request is sent, the API returns 409 Conflict. This protects against breaking DNS validation — resolvers reject responses if the DS record points to keys that no longer exist.
To proceed despite the active DS record, pass force_disable: true in the request body. The zone moves to pending-disabled immediately and transitions to disabled once the DS record is removed at the registrar:
After disabling, wait for the DS record TTL to expire before considering the transition complete — cached records at upstream resolvers remain valid until the TTL passes.